

 Get Started
 Integrate / SDKs
 User Verification
 Business Verification
 Transaction Monitoring
 Changelog

Key Benefits
How to Enable NFC Verification
Native SDK Integration (Recommended)
NFC verification is available through our native SDKs, which provide full access to device NFC capabilities:
The iOS SDK handles all NFC configuration automatically, including:
- ISO7816 application identifiers for ePassports
- Entitlements and capabilities setup
- Real-time chip reading with visual feedback
Web Integration
⚠️ Browser Limitations NFC verification is not available in web browsers due to platform restrictions:For web integrations, NFC verification is automatically skipped and users proceed with standard document + selfie verification.
How It Works
Session Initiation
The user starts the verification process through your app or platform:
- Native SDK: Launch the verification flow directly in your app
- Web/Mobile Web: User is guided to use the Didit App for NFC-enabled verification, or continues with standard verification
Document Photo Capture
The user photographs their ID document, capturing:
- MRZ (Machine Readable Zone) — used to derive chip access keys
- Document front and back images — visual data and security features
- Visual security features — holograms, watermarks, microprint
NFC Support Detection
The system automatically checks device and document compatibility:
If NFC is unavailable, verification continues seamlessly with standard document + biometric verification.
NFC Chip Reading
For compatible devices and documents:
- User is guided to position their document near the phone’s NFC reader
- Visual feedback shows real-time reading progress
- Secure communication is established with the chip using PACE/BAC protocols
Data Extraction
The system extracts comprehensive data from the chip following ICAO 9303 standards:
Cryptographic Verification
The extracted data undergoes rigorous cryptographic verification:
Digital Signature Verification
Digital Signature Verification
Each data group’s hash is verified against the signatures stored in the SOD, ensuring data integrity.
Certificate Chain Validation
Certificate Chain Validation
The chain of trust is validated: Document Certificate → Country Signing CA → ICAO PKD Root, checking against CSCA master lists and the ICAO Public Key Directory.
Certificate Revocation Check
Certificate Revocation Check
Certificates are verified against Certificate Revocation Lists (CRLs) to ensure they haven’t been revoked and the document hasn’t been reported stolen/compromised.
Cross-Validation
Cross-Validation
NFC-extracted data is cross-validated against OCR data from document photos, facial biometric comparison, and MRZ checksum verification.
Result & Confidence Score
The final verification result includes:
Supported Documents
NFC verification works with ePassports and eIDs that contain an NFC chip, typically indicated by this symbol on the document: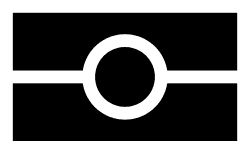
Japan My Number Card (JPKI)
The Japan My Number Card (マイナンバーカード) has a chip, but not an ICAO 9303 one. It holds certificates issued under JPKI, Japan’s public key infrastructure, and private keys that only sign after the holder enters the card’s PIN. Didit reads it in the same NFC step, through JPKI instead of ICAO 9303, and every NFC result says which protocol was used inchip_protocol (icao or jpki).
Requirements
What the person does
Photograph the card
The person captures the My Number Card in the ID verification step, as with any document. Didit recognizes the card and sends a JPKI NFC step instead of a passport chip read.
Enter the card PIN
The SDK asks for the card’s 4-digit PIN (利用者証明用電子証明書の暗証番号). When the NFC node’s
jpki_request_attributes setting is on (the default), it also asks for the signature password, also called the signature PIN (署名用電子証明書の暗証番号, 6 to 16 uppercase letters and numbers).Hold the card to the phone
The SDK reads the card’s certificates, and the card signs a one-time challenge from Didit with its own key. The SDK uploads the certificates and signatures. The PINs only go to the card, never to Didit.
The card counts wrong entries: it locks the 4-digit PIN after 3 in a row and the signature password after 5, and a locked one has to be reset at the holder’s municipal office. After a wrong entry, the SDK shows how many tries are left. It never makes the last try: when only one is left, it stops and tells the person where to reset it. Ask people to have their PIN and signature password ready before they start.
What Didit checks
Each action is a setting on the NFC node, so you can change it to No action, Review or Decline. See NFC warnings and the NFC feature config.
What an unchecked revocation status means
revocation_status: "unchecked" means Didit verified the certificate chain and the card’s signature, but got no answer on whether a certificate has been revoked. A certificate is revoked when, for example, the card is reported lost. Because a revoked card can’t be ruled out, unchecked is never treated as good. It raises JPKI_REVOCATION_UNCHECKED, which sends the NFC step to review by default. Choose a different outcome with jpki_revocation_unchecked_action.
When the certificate chain or the signature is not valid, Didit does not ask about revocation: the status stays unchecked and only the chain or signature warning is raised.
Holder data and privacy
- With
jpki_request_attributeson, the decision includes the holder’s name, date of birth, sex and address from the signature certificate underjpki.attributes. With it off, the person only enters the 4-digit PIN: the read still proves the card and the PIN, but carries no holder data and is not compared with the photo of the card. - The NFC step never reads the card’s 12-digit Individual Number (My Number) from the chip.
- The decision reports what the card proved, never the certificates themselves, their serial numbers or the signatures.