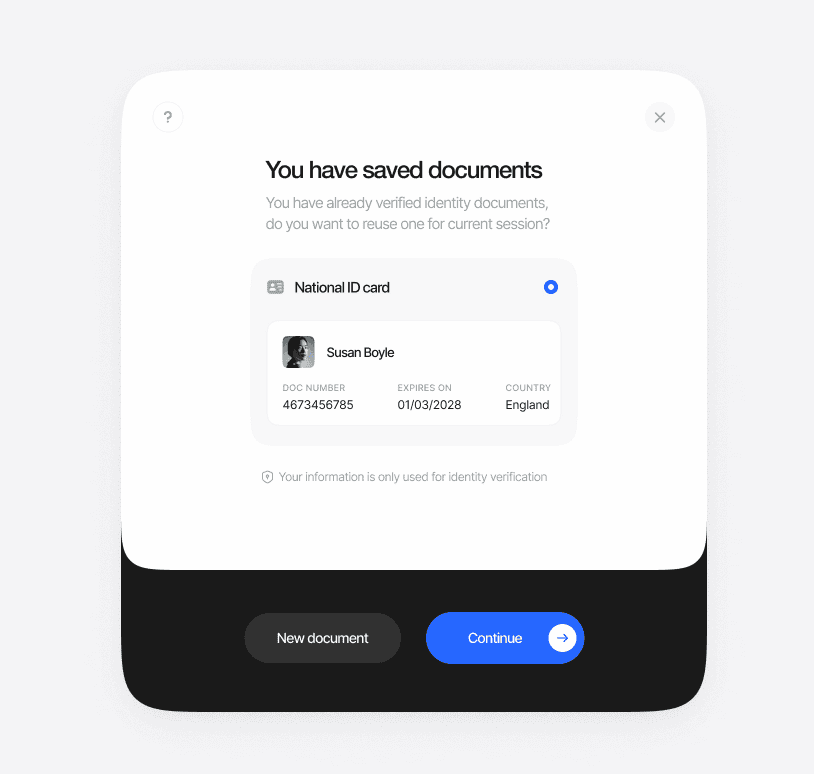
Reusable KYC allows users to verify their identity once and securely share that verification across multiple Didit-integrated applications. This reduces onboarding friction while maintaining security and compliance.
This chapter of the Didit Academy KYB lesson picks up at party verification and reusing KYC sessions.
In the KYB Academy lesson, the 7:04 chapter shows party verification reusing an existing KYC session instead of making a UBO verify twice.
How it works
Initial verification
The user completes a standard KYC process (ID Verification + facial recognition). Verification data is encrypted and stored in the user’s Didit ID, compliant with eIDAS2.
Reuse at a new application
When the user encounters another Didit-integrated application, they select the option to reuse their existing KYC. A quick facial recognition check confirms their identity, and they consent to share specific data.
Instant onboarding
The new application receives the verified KYC information instantly — no document re-upload, no waiting.
Key Benefits
Security and Compliance
Reusable KYC is automatically available to users who have completed an initial verification. Users can choose to reuse their KYC or perform a fresh check at any time. Last modified on October 28, 2026


 Get Started
 Integrate / SDKs
 User Verification
 Business Verification
 Transaction Monitoring
 Changelog